Uncover Past AI Activity.
Strengthen Future Oversight.
AIMS™ Historical Monitoring helps financial institutions identify AI activity, sensitive data exposure indicators, and potential policy concerns within historical vendor logs. Through structured scanning, detailed findings, and examiner-readable audit reports, institutions can better understand past AI usage and maintain a documented record of their oversight activities.
Start With Your Existing Vendor Activity Logs
Create an audit run, select the vendors to review, and upload existing activity logs to begin analyzing historical AI usage.
AIMS™ supports multiple vendors and log formats, including access logs, application logs, transaction extracts, JSON, and text files. Uploaded files are automatically processed in the background, with status indicators tracking their progress.
Detect AI Activity, Sensitive Data, and Potential Risks
Once uploaded, vendor activity logs are analyzed using configurable scanning rules and layered detection methods to uncover AI usage, sensitive information, exposed credentials, and potential policy concerns.
AIMS™ identifies known AI tools, model names, and vendor-specific AI features while scanning for personally identifiable information (PII) and credential exposure. Its detection framework combines pattern matching with additional analytical techniques to surface activity that may otherwise go unnoticed.
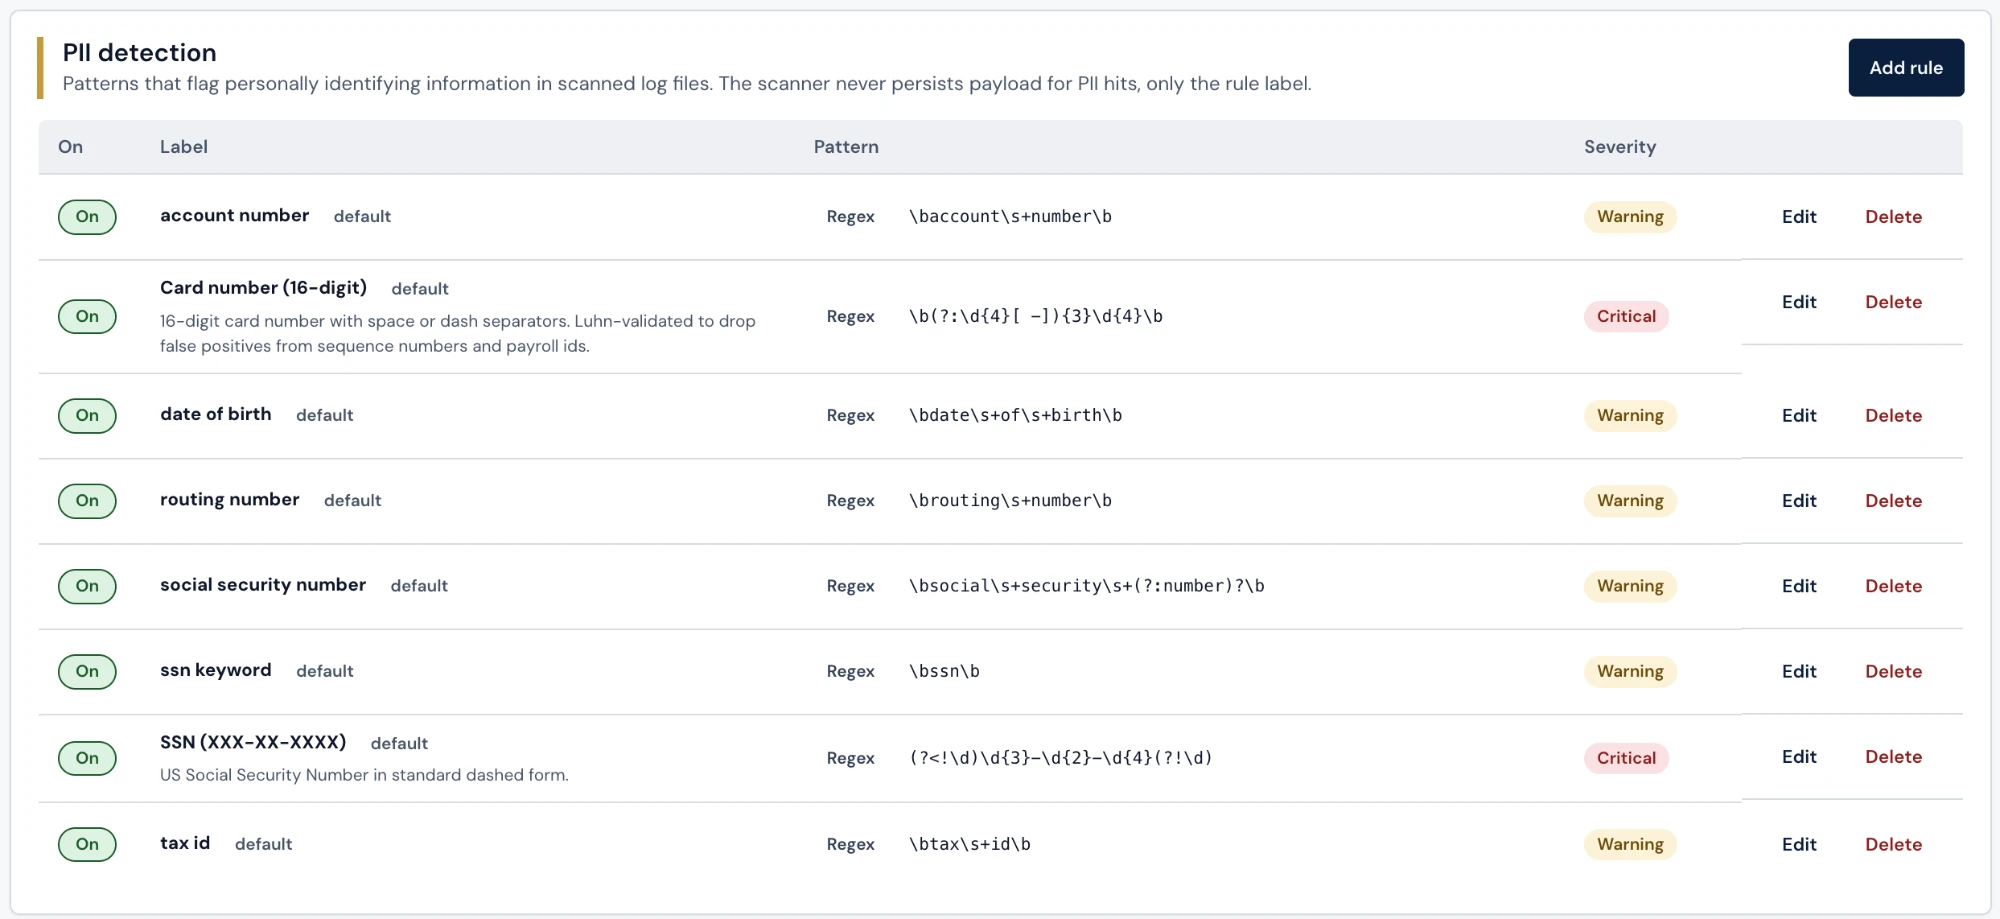
AI & LLM Detection
Identify AI tools, model names, and vendor-specific AI features, including ChatGPT, Claude, Gemini, and Copilot indicators.
Sensitive Data Detection
Flag potential PII exposure, including SSNs, payment card data, account numbers, and other sensitive identifiers.
Credential Exposure
Detect patterns associated with API keys, access tokens, secrets, and other potentially exposed credentials.
Policy Concern Detection
Surface activity matching configured policy rules and supported semantic detection methods.
Turn Audit Findings Into Actionable AI Oversight
AIMS™ consolidates audit findings across vendors, highlighting AI activity, sensitive data exposure, and potential risks. Newly discovered AI vendors are automatically added to the inventory for further evaluation through the AIMS™ AI Risk Score™ workflow.
| Vendor | Events | AI | PII | Status |
|---|---|---|---|---|
| Microsoft 365 Medium · 26 | 11,501 | 2,287 | 785 | Active |
| Salesforce Medium · 37 | 6,865 | 1,356 | 758 | Active |
| Google Workspace Medium · 26 | 5,595 | 955 | 456 | Active |
| ServiceNow Low · 23 | 6,530 | 933 | 343 | Active |
| Box High · 53 | 1,510 | 124 | 46 | Active |
Vendor-Level Findings
Review detected activity and potential exposure across individual vendors.
Detection Breakdown
Examine findings by AI features, models, sensitive data, and detection category.
Inventory Discovery
Automatically identify and add previously untracked AI vendors for evaluation.
Risk Assessment
Route newly discovered vendors into the AIMS™ AI Risk Score™ workflow for further assessment.
Turn Audit Findings Into Examiner-Ready Documentation
AIMS™ generates comprehensive, examiner-readable PDF reports documenting historical AI activity, sensitive data findings, and vendor-level risks. Authorized users can formally attest to completed audits, with reviewer details, timestamps, and SHA-256 verification providing a documented record of oversight.
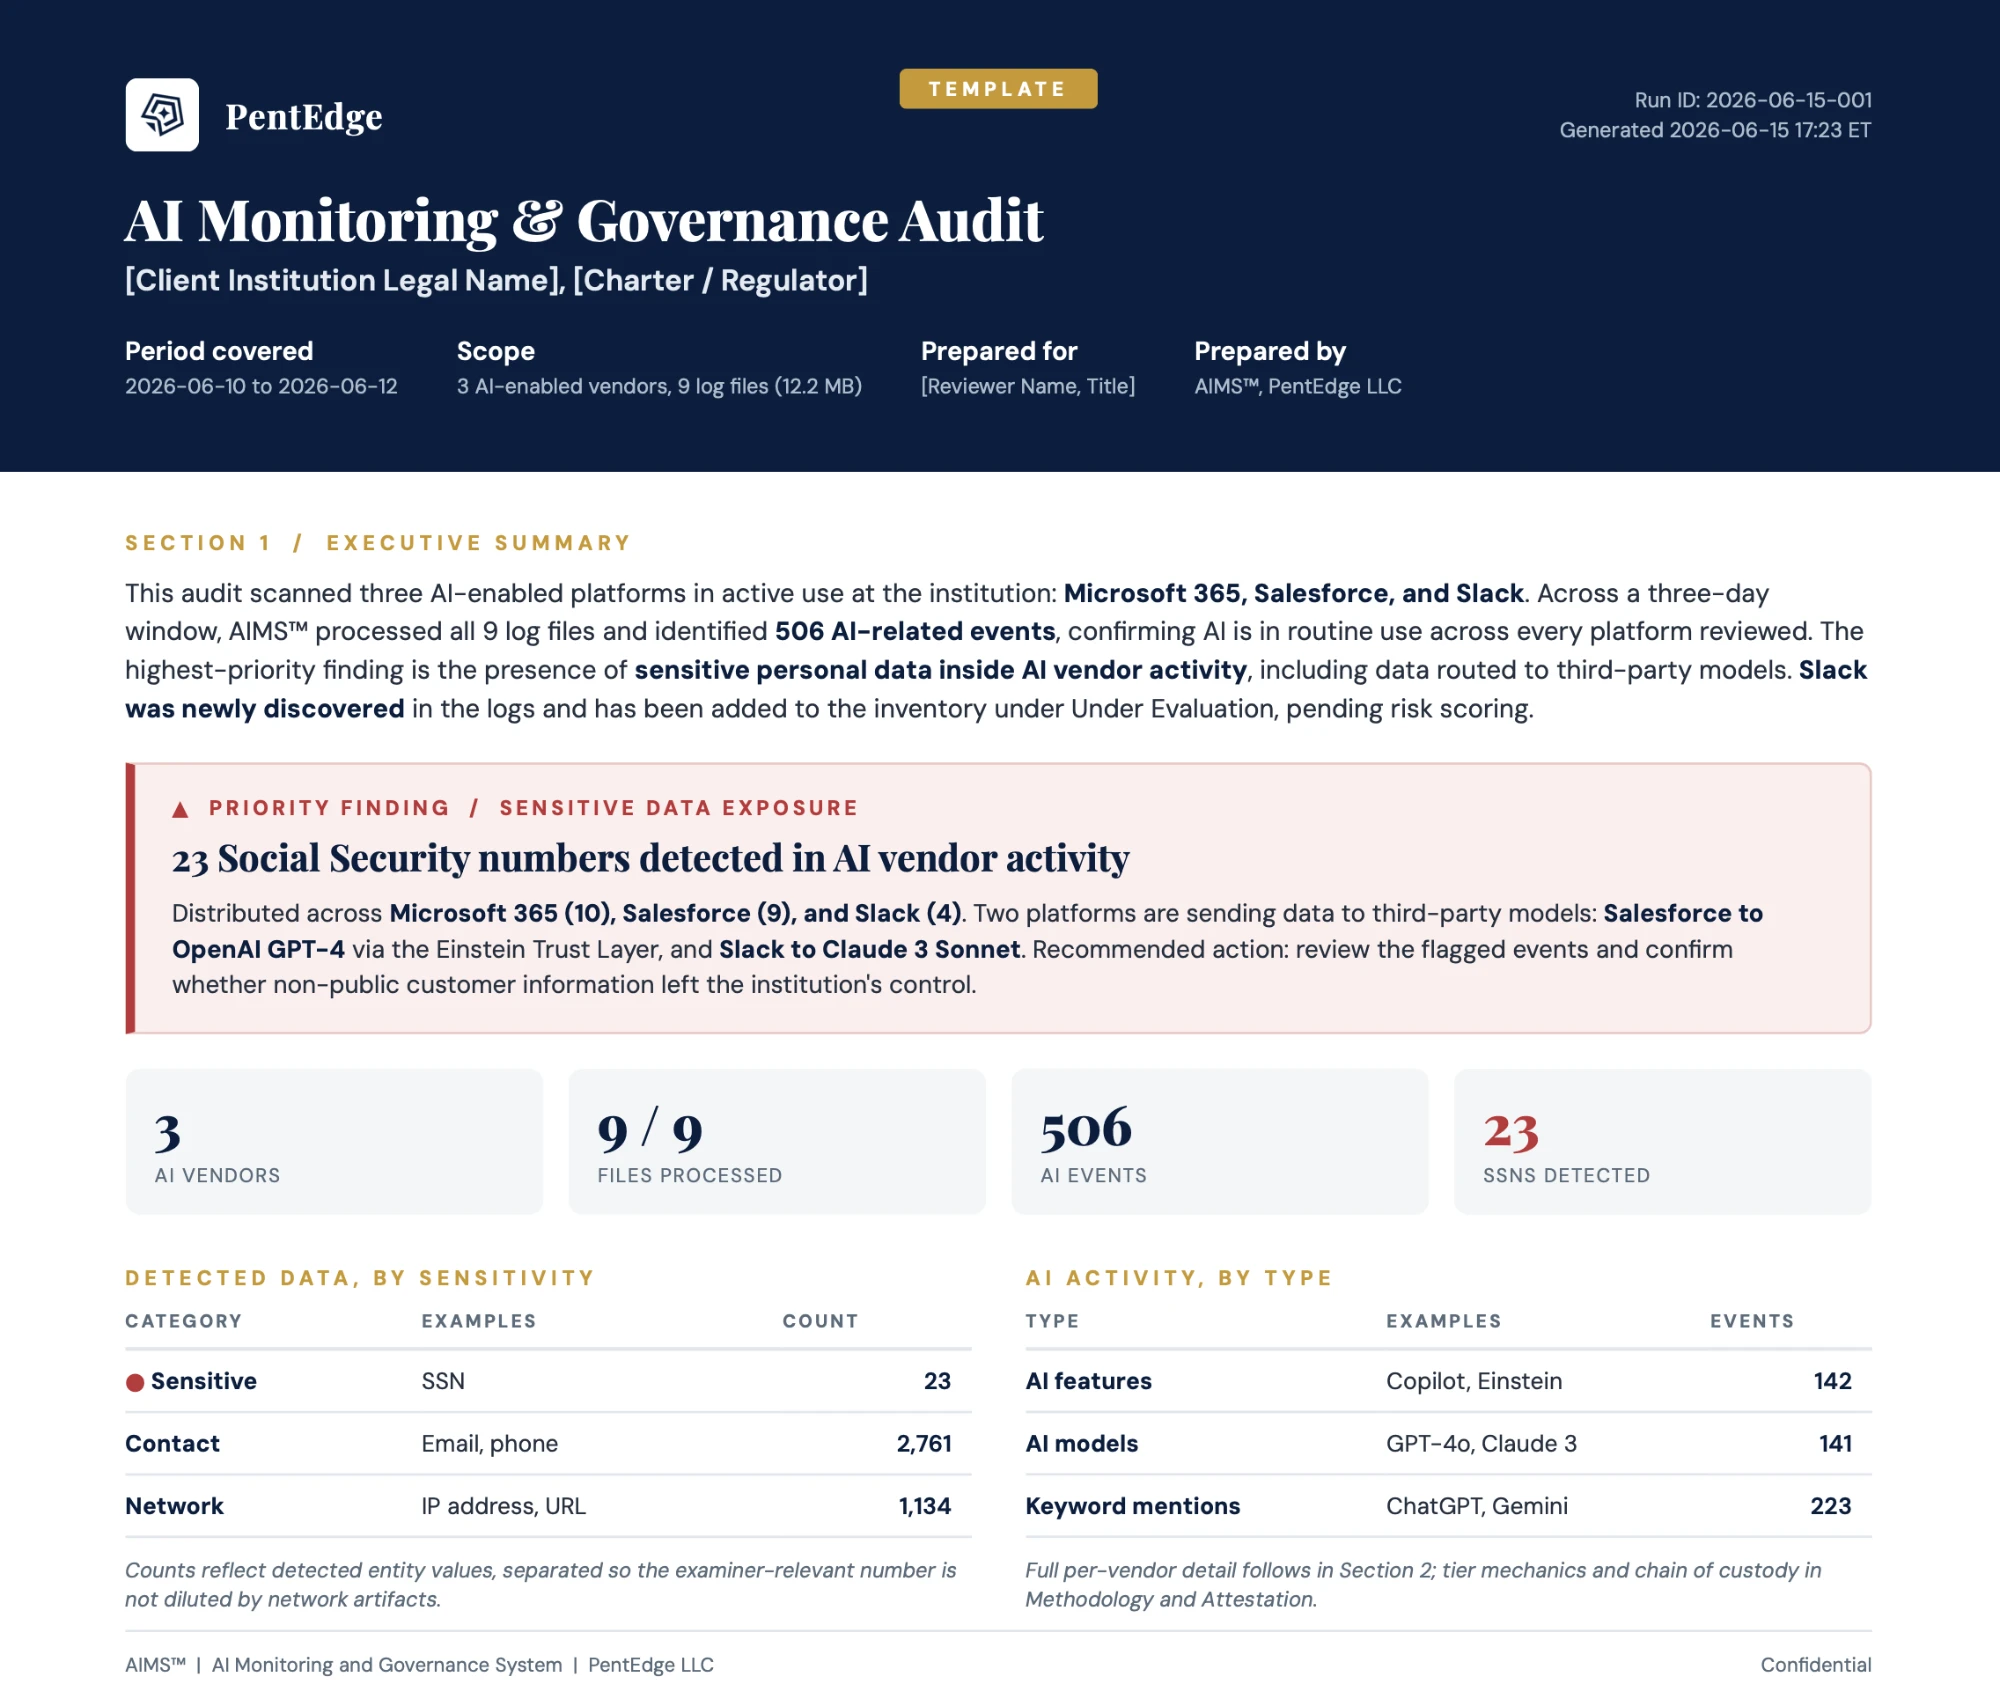
Executive Audit Summary
View key audit metrics and findings.
Detailed Vendor Findings
Explore AI activity and sensitive data by vendor.
Detection Transparency
Review scanning methods and detection results.
Attestation & Integrity
Verify sign-off and detect changes to findings.